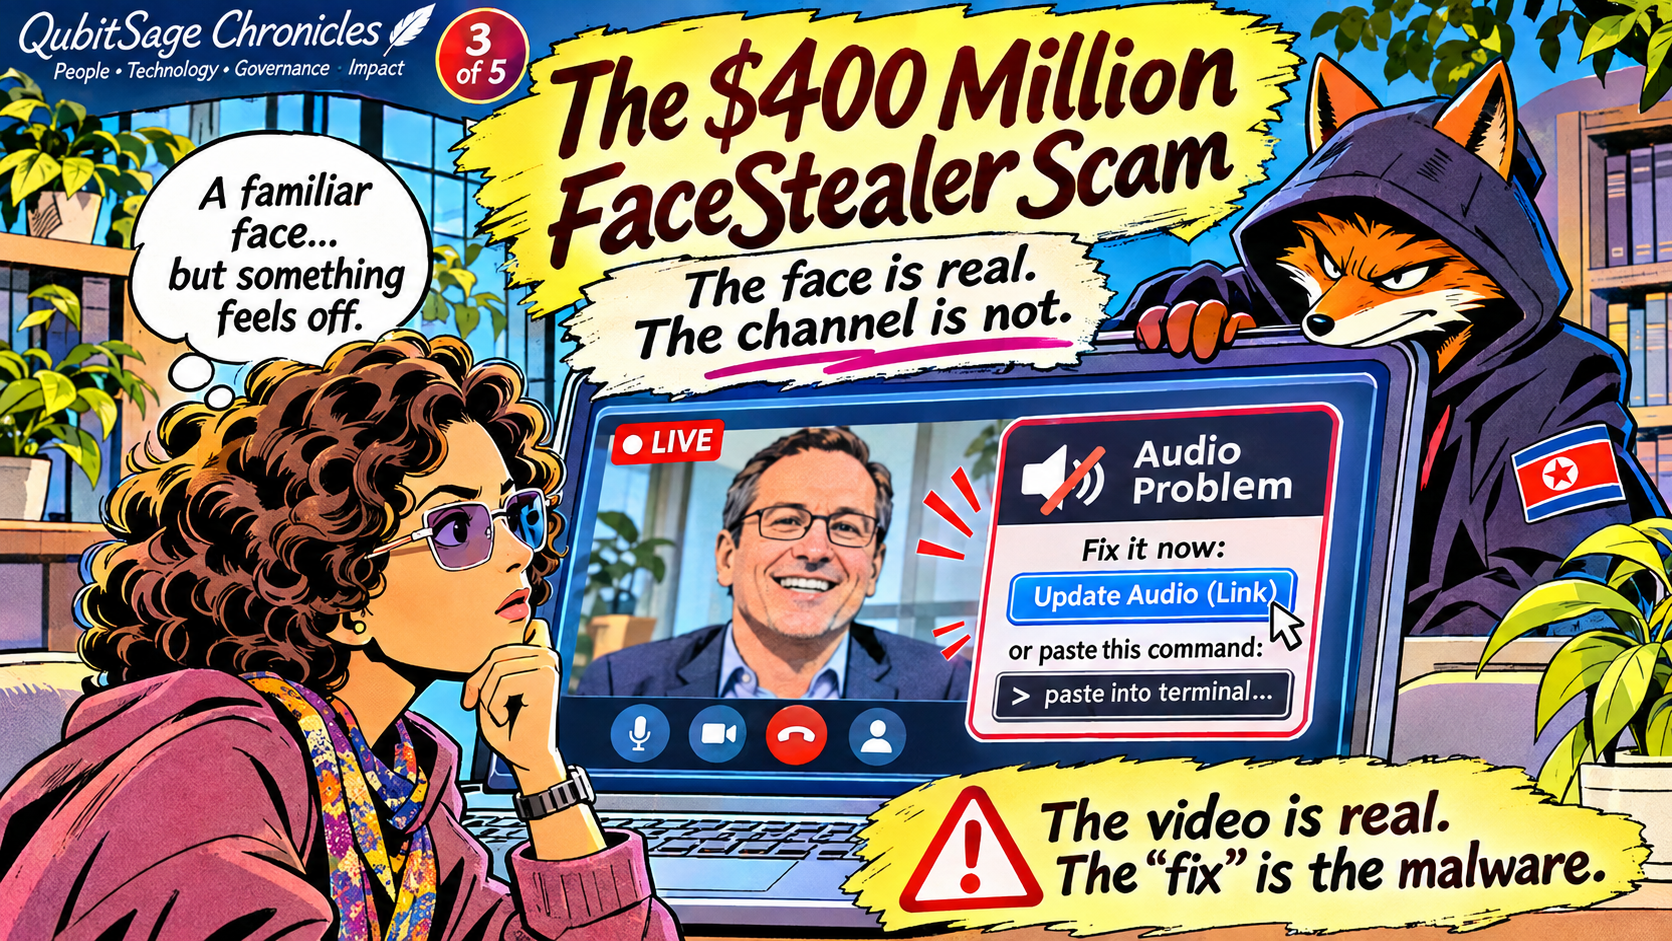
The FBI Just Named a $400 Million Scam, and the Scariest Part Is Not the Deepfakes The FBI named it FaceStealer.
On November 12, 2026, The Bureau published FLASH AC-111226-MS, and the Department of Justice announced related actions the same day. (Sources section at the end for references)
North Korean actors, the groups tracked as Sapphire Sleet, UNC1069, Dangerous Password, CryptoCore, APT38, BlueNoroff, and Stardust Chollima, stole more than $400 million(hmm…wonder how many zeros that has) in cryptocurrency over 18 months.
The weapon was not a zero-day. It was a…drumroll…. A Meeting Invitation & VIDEO CALL 🤙
Nefarious actors (ab)using AI and I bet it wasn’t even too hard.
Here’s the lowdown as I gather:
Step 1: The Hijack
The attackers take over a real account on Telegram, LinkedIn, Slack, or Discord. The messages that follow come from someone you know, or someone whose name you recognize. That is the whole point.

Step 2: The Lure
The hijacked account invites you to a meeting on Zoom, Teams, or Meet. The invitation looks ordinary. The meeting page lives on a typo-squatted domain, names like uu01webzoom.us and teams.livemeet.us, built to look exactly like the real thing.

Step 3: The Fake Meeting
You join, and a video plays. It is a prerecorded webcam recording of a real victim, played back to simulate a live call. Sometimes there are several fake participants, to add pressure and make the room feel real.

Step 4: The Trap
An audio error appears. The fix on screen tells you to click an update prompt, or to paste a code into your terminal. That fix is the MALWARE: a cookie harvester, keyloggers, screen capturers, a backdoor. One paste, and they are inside your machine. BOOM!

Step 5: The Theft
They do not steal at once. The attackers wait months, sometimes more than a year, and take the money once the wallet balances have grown. That patience is part of the design.

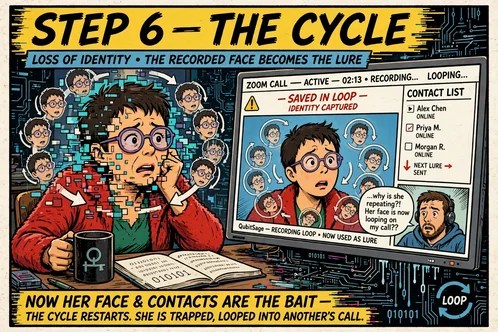
Step 6: The Cycle
Your webcam was being recorded from the moment you clicked the link. Your face, and your contact list, become the next lure. The victim becomes the next Sarah, and the loop starts again. The FBI has seized more than 900 victim videos.
Now What? Course correction and FIX!
The faces are mostly real. Deepfakes are just a part of the story, the Justice Department calls the capability “super intelligence-enabled“(eh!? more like sneaky evilness enabled) and they are used for well-known crypto figures.(luckily i don’t fall in that bracket…sigh…)
But the scheme sadly runs on genuine recorded video of real victims. If you are watching for a deepfake, you are watching for the wrong thing. The face on screen is REAL! Its a Swetha or a Sarah you know and work with, a colleage you trust enough to not think twice before clicking a link from their email, they may be, I am(maybe?!) BUT that call is NOT!
Two numbers to keep separate:
1. $400 million-plus is FaceStealer over 18 months.
2. The $1.2 billion seized or restrained, and the roughly $6 billion Binance theft from October 29,
Two separate North Korean cases announced the same day.
I know, so many chaotic cases in the latter half of 2026(personally too, lately theres just too many doomsday news all around us that their seriousness and assoccated risks due to exposures get lost or barely grab our attention, before we even know what happened, we see a gazillion alerts-

FLASH NEWS every sec, splattered all across social media whether we like or not, follow or not. Each one diverting our attention from news that demands our undivided attention.
Our attention is getting sparce, hence why this rather simple hacking works so well, and it is the part that should worry anyone who takes meetings for a living. Hackers scheme does not attack the software when you join the call, it attacks the moment you decide the face on screen is the person you know and TRUST and decide to resolve their identity on your meeting video screen…tsk tsk tsk…
The HUMAN on the call now has to be the last check, and the check has to be awake to the mechanism, not the face.
Three rules to follow per the FBI’s guidance:
1. Join through the official app, with an invite code. Never join from a link.
2. Keep your webcam off until you can see, hear, and talk to the inviter.
3. Never paste code or run a script to fix a meeting.
Update the app separately, on your own time not during the meeting.
Some more health checks/ routine habits worth building:
- confirm meetings from infrequent or new contacts through a second channel before you join, and
- turn on MFA and login alerts on Telegram, WhatsApp, Slack, and LinkedIn
I know, these are too much, but oh well! Such are our needs and perils.
If it already happened to you, start on the remediation work -> Set up a new wallet with new seed phrases on a clean device, change your passwords, log out of all sessions, add MFA, warn your contacts and your employer, and report it at IC3.gov with the keyword “FaceStealer.”
This one lands close to home for me. :/ A job search runs on meeting invites from new contacts and recruiters, and that is the exact lure vector. GULP! 😓
The armor I wear can’t be suspision of every face, thatd make our lives a living prison and our existence filled with fear and uncertainity. NOT conducive to progress. Instead its a small set of habits, applied every time, without fail, on purpose..before the gentle colleagues profile picture and familiar face gets a vote of confidence and mindless click! As I said in prior posts, several times:
TRUST, BUT ALWAYS VERIFY
ALLOW, BUT AFTER AUDIT
Sources:
| Title | Link | Incident |
|---|---|---|
| FBI FLASH AC-111226-MS (Nov 12, 2026) | https://www.ic3.gov/CSA/2026/261112.pdf | The FBI’s FaceStealer Alert: How the fake video calls work and how to defend against them. |
| DOJ press release: Actions to Disrupt North Korea’s Massive Theft of Cryptocurrency (Nov 12, 2026) | https://www.justice.gov/opa/pr/justice-department-announces-actions-disrupt-north-koreas-massive-theft-cryptocurrency | DOJ’s announcement covering the FaceStealer disruption and the separate $6B Binance theft by TraderTraitor. |
| FBI Los Angeles PSA video (Nov 12, 2026) | https://www.facebook.com/reel/1102951969229867/ | FBI Los Angeles video warning from SAC Jeremy Robertson, same facts as the FLASH, in video form. |
| FBI FaceStealer resource page (Nov 12, 2026) | https://www.fbi.gov/facestealer | The FBI’s central resource page for the scheme, with the FLASH and reporting guidance. |
| IC3 PSA: FBI Warns of Scammers Impersonating the IC3 (Jul 2026) | https://www.ic3.gov/PSA/2026/PSA260720 | FBI warning that scammers impersonate the FBI and IC3, including AI deepfake videos used in real-time video chats. |
| IC3 PSA: Senior U.S. Officials Continue to be Impersonated (Dec 19, 2025) | https://www.ic3.gov, alert I-121925-PSA | FBI warning on AI-generated voice and text messages impersonating senior U.S. officials. |
| IC3 PSA: Criminals Use Generative AI to Facilitate Financial Fraud (Dec 3, 2024) | https://www.ic3.gov/PSA/2024/PSA241203 | The FBI’s foundational warning on criminals using generative AI for fraud, including fake live video calls with executives. |
And for all the agentic experimenters out there(ahem..me included), careful what you build. Its simple really, just choose be good and do good, for yourselves & others, each time, every time.


Leave a Reply